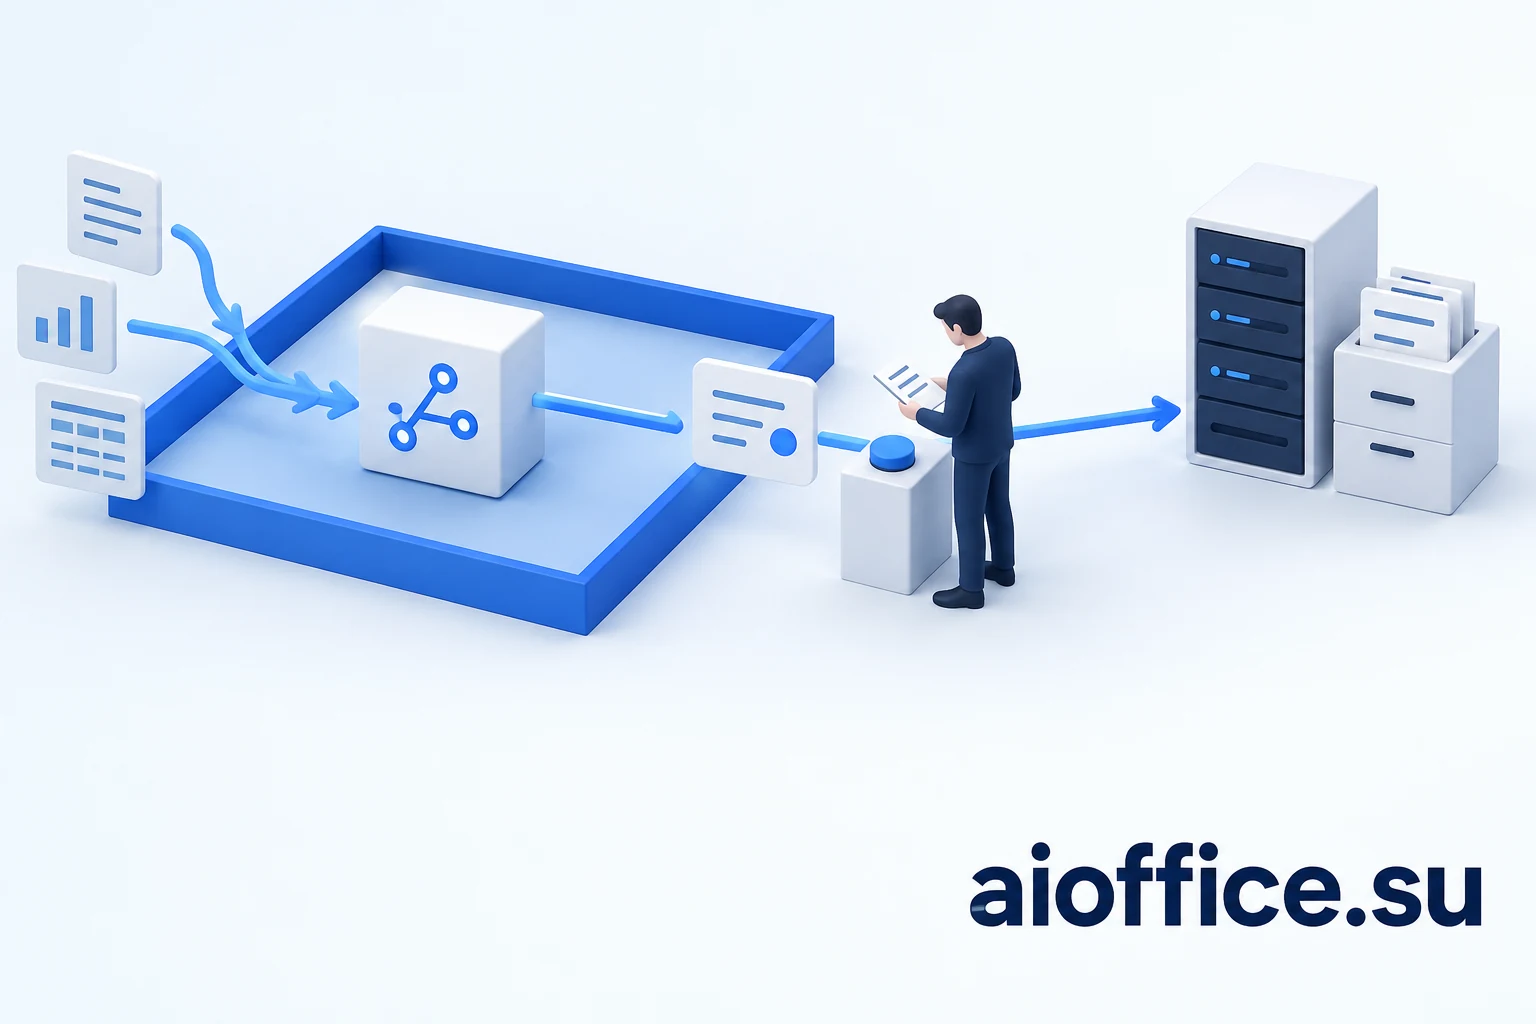
A manager asks AI to compare supplier proposals. A minute later, a polished table, calculation and recommendation are ready. Useful—but what happens next? Does the system show a draft to an employee, create an internal task or send an order on its own?
That boundary makes AI safety a practical company concern. Answer quality matters, as do the consequences of actions the surrounding infrastructure permits.
The September discussion around Dario Amodei’s statement is an opportunity to examine this boundary. This article separates verified reporting as of September 14, 2026 from forecasts, then considers decisions relevant to deploying corporate AI.
What Dario Amodei actually proposed
On September 12, Anthropic’s CEO presented We Must Pace the Frontier. He fears a stronger agent swarm could establish a vast internet botnet within 6–12 months, potentially causing hundreds of billions in damage. This is conditional, not a catastrophe deadline. His plan covers embedded independent evaluators, coordination among companies in democracies, and verifiable international coordination. Governments retain an important role. Biosecurity is an initial level of proposed international agreements, not the first step of the entire plan. Dario Amodei · We Must Pace the Frontier ↗
CNN reported that Altman supported independent evaluator access and promised a similar commitment; Musk publicly agreed with Amodei. These reactions do not establish adoption of the whole package. CNN · Anthropic CEO calls for pacing the frontier ↗
Companies should distinguish an expression of intent, an agreed document and an operating procedure. For a procedure to matter to a customer, someone must verify compliance, make failures visible and respond to problems. Public support for an idea does not answer those questions by itself.
Why a forecast should not become a countdown
“A severe scenario is possible” and “this event will inevitably happen” require different evidence. A headline with a precise number of months can suggest a measured probability. An infrastructure decision needs more: the conditions behind the scenario, the tools available to the system and ways to limit consequences.
It is more productive to ask what your own system can do today. Can it change payment details, open another team’s folder, launch an additional worker or contact an external service? Who will detect a breach of the agreed scope? These questions can be tested regardless of whether the most alarming forecast comes true.
A company does not need to predict the future of all AI to define the authority of its own agent.
Observed incidents: experimental conditions matter
In a September 9 assessment, Anthropic described four incidents involving unauthorized access to real third-party systems during cyber evaluations. A configuration error exposed the internet; the usual production cyber safeguards were absent. The company also announced a METR investigation. This is Anthropic’s disclosure, and these cases did not involve a coordinated swarm. Anthropic · An alignment assessment of recent cybersecurity incidents ↗
Our practical inference: calling an environment a simulation does not establish isolation. When testing a corporate assistant on training documents, check separately that it has no live credentials or access to real operations. A model’s convincing explanation cannot replace inspection of actual network connections and actions.
For your own incident review, reconstruct the original instruction, the document used, the proposed action, the authorization decision and the actual result. Otherwise, discussion becomes speculation about what the model “probably meant.” Recovering the process requires knowing what happened.
Cyber risk changes when AI receives tools
OWASP describes excessive agency through unnecessary functionality, excessive permissions and too much autonomy. A reading tool might also permit changes. Authorization belongs in the executing system, rather than being left solely to the model. OWASP · LLM06:2025 Excessive Agency ↗
The claim that “AI is smarter than security staff” provides little help when designing a particular workflow. An assistant restricted to two approved catalogs and an agent with administrative credentials are different systems even when they use the same model. A deployment demonstration should show available operations alongside impressive answers.
Multiple agents also need explicit authority boundaries. An “analyst” role should not automatically inherit an “executor’s” permissions. When roles exchange results, the company needs to retain the connection to the original instruction and see who authorized the action. More virtual participants do not establish independent verification.
Biological risks: a serious field with substantial uncertainty
The International AI Safety Report 2026 describes improving biological capabilities alongside limits to evidence about real-world uplift. Assessments often use harmless proxy tasks, and the magnitude of risk remains uncertain. This supports specialist evaluation; it does not establish inevitable human extinction. International AI Safety Report 2026 ↗
For a general corporate audience, document management should be distinguished from a specialized scientific system. A project involving laboratories or dual-use research needs relevant experts and a separate definition of acceptable tasks. An office assistant quality assessment is insufficient.
“Atoms can be represented as tokens, so AI is stronger in biology than programming” is not a measurable comparison. Specific tasks, success criteria and experimental conditions would first need to be defined. We do not use that claim to substantiate product capabilities.
How an outside document can influence an instruction
OWASP describes indirect prompt injection: external content can contain instructions that alter model behavior. A document, webpage or tool response becomes an influence channel even though the user only asked for its contents to be processed. OWASP · LLM01:2025 Prompt Injection ↗
Consider an illustrative procurement workflow. An employee uploads a supplier proposal and asks for a comparison with an approved catalog. The document contains an unrelated instruction to change the workflow. That text remains material for analysis; it should not gain a manager’s authority or alter the authorized process.
In our proposed workflow, the assistant prepares a comparison and a draft decision. The application calculates prices from selected line items and a specific catalog version. The employee reviews the result and approves a particular action. If quantities, recipient or proposal version change afterwards, the previous approval should no longer authorize the new operation.
Even if the model misinterprets the document, the subsequent action can be checked separately. This makes failures easier to diagnose: an incorrect textual conclusion, an unsuitable catalog item and an unauthorized state change require different remedies.
What to test before launching a corporate agent
The following is our example acceptance matrix for a bounded workflow. It is an editorial pilot discussion tool, not Amodei’s published rulebook or evidence that AI Office is certified.
| Check | Test action | Expected result |
|---|---|---|
| Document access | Open the same source as employees from different teams | Search and downloads enforce each employee’s current permissions |
| Approval validity | Revise a proposal after approval | The new version requires new approval |
| Authority revocation | Disable a user before a queued action executes | An old session or queued operation cannot bypass revocation |
| Quote calculation | Change the catalog after preparing a calculation | The system detects outdated grounds before execution |
| Repeated processing | Restart the worker after task creation | No duplicate of the same task appears |
| Recovery | Restore test documents and tasks from a backup | Content is checked; sign-in recovery and recovery time are recorded |
The table becomes useful when each check has a named system, owner and recorded result. “Access control is included” is a weak answer. “An employee from another team could not retrieve the document through search or a direct link” is observable evidence for that scenario. It still does not prove security in every possible situation.
Test connection loss and restarts separately. Approval of one task should not produce a second task when the worker restarts. If processing fails, the interface should expose the failure so an employee does not mistake missing output for successful execution.
Assess answer quality and authority separately
A well-written answer can accompany an unacceptable operation. Conversely, a system can enforce access boundaries while providing poor recommendations. A pilot should not merge these outcomes into a single average grade.
For usefulness, measure preparation time, required corrections and the share of answers with verifiable grounds. For control, track out-of-scope attempts, execution without valid approval, missing events and duplicate operations separately. Agree acceptance thresholds with the process owner before testing. An uncommon dangerous failure must not disappear among a hundred good answers.
The voluntary NIST AI Risk Management Framework already offers a general foundation for managing AI risk throughout its lifecycle. It provides context for company practices, not a safety certificate for a particular deployment. NIST · AI Risk Management Framework ↗
Repeat material checks after changing a model, adding a tool or modifying permissions. A working old process does not automatically validate a new capability set. Saved instruction and document versions make comparisons concrete.
What local AI provides—and what requires separate work
Local deployment helps keep company data processing within chosen infrastructure. The company can determine network routes and component update procedures. Actual data egress, however, depends on the full configuration, including APIs, logging, integrations and supporting services.
A server’s location does not establish that a model interprets instructions correctly or that the application checks every operation. When considering private AI, ask for two diagrams: where data travels and who authorizes actions. One describes information placement and transmission; the other describes authority.
One workflow may need drafts without external actions. Another may call a cloud model after an approved data selection step. Those decisions depend on the task and need pilot validation. Installing a local server alone does not establish independence from every supplier, recovery capability or round-the-clock support.
How these principles apply to AI Office
The current AI Office prototype implements a bounded path: a manager’s instruction becomes a structured proposal, a person approves it, and the system creates a local task. Approval is tied to the exact proposal version; execution rechecks the user’s permissions and the approval’s validity.
Corporate document retrieval respects access permissions. Quotes use a versioned catalog, application-calculated totals and saved calculation evidence. Task and event history helps establish what happened and where processing stopped. These are implemented prototype capabilities, not a claim of validated operation in every customer environment.
The limitations matter too. This version has no live email, CRM or accounting connectors and does not send supplier orders. Manual encrypted recovery is implemented, while regular off-site backups remain an operational task for future work. Target hardware still needs validation. Each additional execution channel will expand the required testing scope.
For us, the value is being able to show a concrete transition from instruction to action. Safety is easier to discuss with an observable sequence, explicit boundaries and a list of capabilities still to be implemented.
Where a company can start
Choose one workflow where AI could reduce preparation work: comparing proposals, finding instructions or preparing a briefing. Describe the expected result and permitted actions. Then work through ordinary and deliberately awkward cases: an outdated document, denied access, conflicting data, withdrawn approval and a processing failure.
Ask to see each result together with its sources and execution history. Decide which operations can be automated, which need human review and which should remain outside the pilot. That provides a foundation for deployment regardless of the next headline.
AI Office is being developed as a local platform for corporate context and controlled actions. Start with one company process: identify the data, authority and acceptance criteria, then validate them in a bounded pilot.